Department of Defense Requests $30 Million for AI-Enhanced Deception Detection System
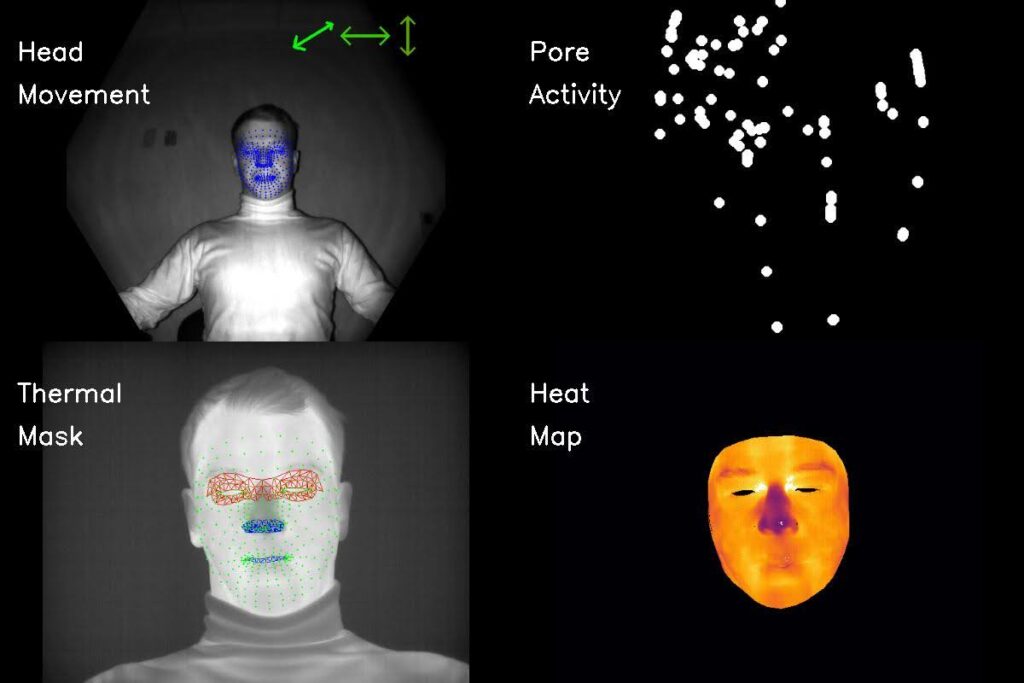
Contextual Background: The Evolution of Lie Detection Technology In recent years, the U.S. Department of Defense (DoD) has signaled a shift towards advanced technological solutions to enhance security measures within its ranks. This trend is underscored by a proposal from the Pentagon seeking $30 million to develop an AI-powered lie detection system, termed Polygraph+. This initiative, spearheaded by the Defense Counterintelligence and Security Agency (DCSA), emerges amidst heightened scrutiny over security leaks, particularly as the department grapples with ongoing tensions, such as those surrounding military engagements in Iran. Traditional polygraph tests, which have been utilized for decades, are increasingly viewed as inadequate in addressing contemporary challenges related to employee vetting and insider threat detection. Main Goal: Enhancing Security through AI Innovations The primary objective of the proposed AI-powered lie detector is to improve the accuracy and reliability of deception detection within the DoD. By integrating artificial intelligence with physiological data analysis, the Pentagon aims to create a more effective screening tool for prospective employees and current personnel. Achieving this goal entails harnessing cutting-edge technologies that can analyze a broader range of physiological indicators, moving beyond the limitations of traditional polygraphs, which primarily measure heart rate, blood pressure, and galvanic skin response. Advantages of AI-Powered Lie Detection Increased Accuracy: Current methodologies, relying on the polygraph, are challenged for their reliability. Reports indicate that the scientific basis for polygraph efficacy is weak, with the National Research Council categorizing its effectiveness as “weak at best.” AI systems could potentially enhance accuracy by incorporating multiple data points and machine learning algorithms to identify patterns associated with deceptive behavior. Objective Analysis: Unlike traditional polygraphs, which can suffer from subjective interpretations by examiners, AI technologies can offer a more standardized approach to data analysis. This could mitigate biases that often arise during human assessments, particularly regarding demographic factors. Scalability: AI systems can process vast amounts of data more efficiently than human examiners, which is crucial given the Department of Defense’s workforce of approximately 2.8 million individuals. This scalability could lead to a more comprehensive screening process while reducing the potential for false accusations stemming from inaccuracies. Innovation in Methodologies: The initiative reflects a broader trend within the DoD to explore novel technologies for security applications. By selecting companies like Presage Technologies and Altec Research, which are developing non-contact sensing technologies, the Pentagon is positioning itself at the forefront of technological innovation in security. Limitations and Caveats Despite the potential advantages of AI lie detection systems, several limitations warrant consideration. The reliability of AI models heavily depends on the quality of the data used for training. If the data lacks diversity or is biased, the outcomes may perpetuate existing disparities. Moreover, the ethical implications of AI surveillance and privacy concerns must be addressed to ensure that the deployment of such technologies does not infringe on individual rights. Future Implications: The Role of AI in Security and Deception Detection The integration of AI into lie detection technology represents a significant paradigm shift that could reshape the landscape of security protocols within the DoD and beyond. As AI continues to evolve, the potential for enhanced predictive analytics and real-time monitoring could lead to a more proactive approach in identifying insider threats. Furthermore, advancements in AI may drive innovations in related fields, such as criminal justice and corporate security, expanding the applicability of these technologies. However, ongoing research and dialogue are essential to navigate the ethical and practical considerations associated with these developments. Disclaimer The content on this site is generated using AI technology that analyzes publicly available blog posts to extract and present key takeaways. We do not own, endorse, or claim intellectual property rights to the original blog content. Full credit is given to original authors and sources where applicable. Our summaries are intended solely for informational and educational purposes, offering AI-generated insights in a condensed format. They are not meant to substitute or replicate the full context of the original material. If you are a content owner and wish to request changes or removal, please contact us directly. Source link : Click Here